Human Accountability, AI Speed
SHQ Axcel assembles incident context for analyst validation, reducing investigation time and improving response accuracy.

24/7 detection and response that goes beyond containing threats. We fix what we find, using every incident to strengthen your defenses and make the next attack less likely.
Every incident drives the closing of gaps and strengthening of controls across your entire security program, continuously reducing the likelihood of another event.
By fixing what we find, ensure the same issues don’t waste time and resources.
Global intelligence, AI-accelerated context, and deep knowledge of your environment allows us to see and respond to threats faster.
We own the results of our response by demonstrating your security improvement, not just reporting on activity.
We continuously tune and optimize your existing tools. Unlike vendor-led MDR, you own all the improvements we make in your systems.
Continuous monitoring powered by 6 global SecOps centers and SecurityHQ Adversary Labs, expert response owned by a designated cyber consultant.
SHQ Axcel correlates threat and exposure context, while experienced analysts validate every alert and make every decision.
SHQ Axcel assembles incident context for analyst validation, reducing investigation time and improving response accuracy.
Continuous tuning and log optimization reduce noise and ingestion costs without sacrificing critical visibility.
Every investigation informs corrective actions, stronger detections, and proactive hunts to reduce the likelihood of repeat attacks.
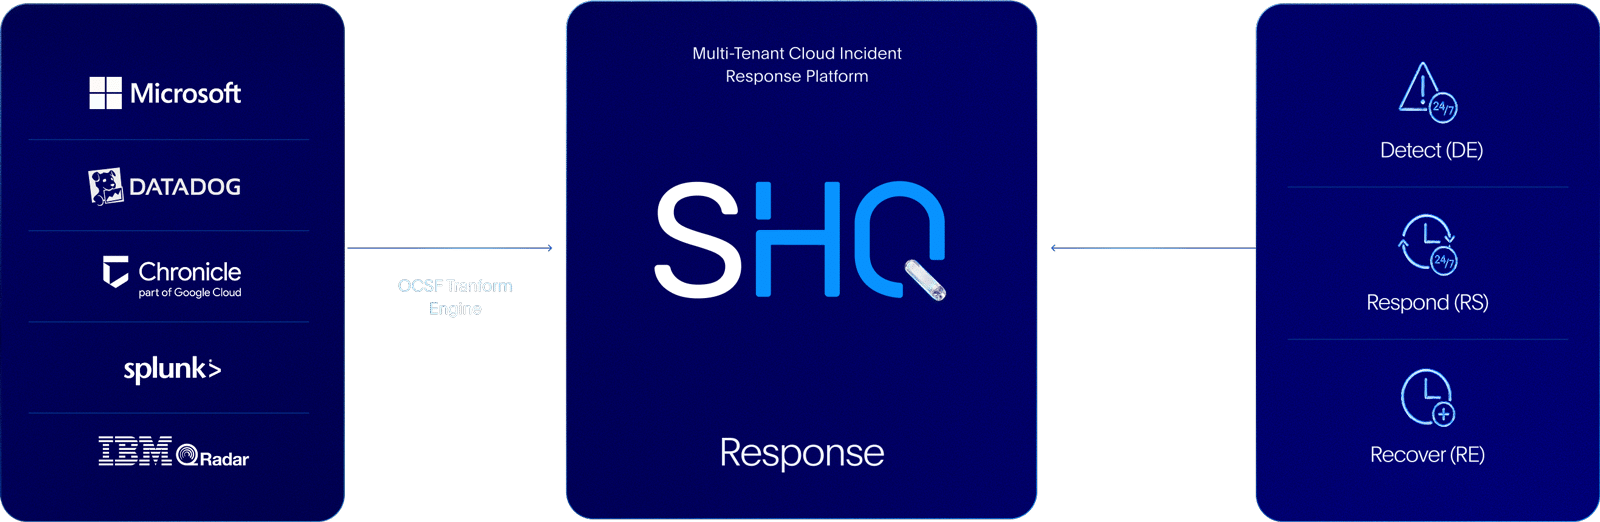
Threat intelligence, exposure findings, and incident learnings inform improvements across connected security technologies.
We don’t stop at resolving the immediate threat. Every incident becomes an opportunity to fix underlying weaknesses and strengthen security across your environment.
We go beyond containment to address root causes, coordinate corrective actions, and validate improvements.
Our Adversary Labs turns findings from global investigations into new detections and proactive hunts across your environment.
We continuously tune detections, configurations, and playbooks, applying what we learn to improve security over time.
Designated experts know your environment, make critical decisions, and stay accountable for outcomes across our global SOCs.
Constant monitoring and analysis of endpoint devices to detect and respond to threats. By utilizing advanced tools and expertise, we help organizations quickly identify security incidents, mitigate risks, and improve their overall endpoint security posture.
With digital forensics and dynamic threat hunting, uncover attack paths beyond normal security logging, detect breaches, and take proactive actions to contain threats.
 RESOURCES
MDR services detect, investigate and respond to threats across an environment on a 24/7 basis. SecurityHQ pairs SOC analysts with ML-driven analytics to catch threats early and contain them before they spread.
MDR stands for managed detection and response, a service that monitors an environment continuously and acts on threats as they emerge. SecurityHQ's MDR service integrates with existing SIEM technology regardless of vendor, so organizations do not need to replace their current tools.
EDR is a technology that monitors endpoint activity, while MDR is a managed service that includes 24/7 detection, investigation and incident response built around that technology and more. SecurityHQ's MDR service layers threat detection and response on top of a technology-agnostic SIEM integration.
SecurityHQ's MDR service monitors an environment continuously, applies ML-driven analytics to flag suspicious activity and investigates alerts before they reach a client's team. Analysts then respond directly to contain confirmed threats, cutting the time between detection and action.
Traditional tools generate alerts, but MDR adds the analysts and processes needed to investigate and act on them 24/7. SecurityHQ's approach combines continuous monitoring with incident response, closing the gap that tools alone leave open.
Organizations should look for 24/7 threat detection and incident response, not just alerting during business hours. SecurityHQ also emphasizes technology-agnostic SIEM integration and low cost of ownership, so clients avoid rebuilding their existing stack.


